
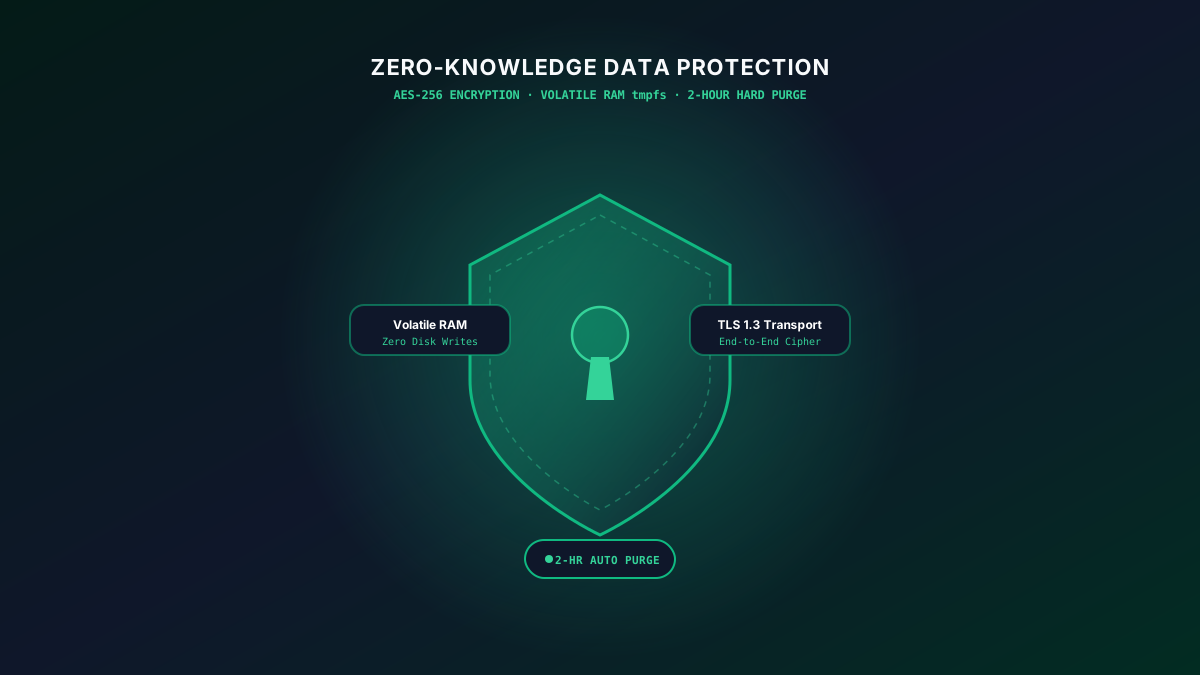
Zero-Trust Architecture: Why Document Privacy Demands Mathematical Isolation
In an era dominated by sophisticated supply-chain cyber attacks and pervasive corporate surveillance, security cannot rely on policy promises or marketing assurances. True data protection must be mathematically enforced at every stage of the document lifecycle: in transit, during execution, and upon job termination.
SwiftFileConvert operates on a strict Zero-Trust Processing Protocol: files uploaded to our cluster are treated as confidential, untrusted payloads that are encrypted end-to-end, transcoded in isolated memory sandboxes, and permanently destroyed within 2 hours of processing.
Cryptographic Perimeter & Ephemeral Lifecycle
ECDHE key exchange with ChaCha20-Poly1305 and AES-GCM cipher suites. Complete forward secrecy against interception.
Transcoding occurs entirely within volatile RAM disk containers without writing unencrypted state to non-volatile disk.
Immutable 2-hour TTL timer triggers cryptographic overwrite and immediate memory page deallocation.
1. Cryptographic Safeguards: In-Transit and At-Rest Encryption
SwiftFileConvert mandates TLS 1.3 encryption for all network streams. Legacy SSL protocols and insecure ciphers (such as RC4, 3DES, or unauthenticated CBC modes) are blocked at our load balancer edge. At rest, uploaded artifacts are secured with AES-256-GCM authenticated encryption using distinct, ephemeral cryptographic initialization vectors (IV) for every file.
2. Zero-Trace Ephemeral In-Memory Storage & 2-Hour Auto-Purge
Unlike conventional web services that store customer files in persistent cloud object buckets for days or weeks, SwiftFileConvert enforces strict ephemeral storage. Every conversion job receives a cryptographic Time-To-Live (TTL) token:
- Volatile Memory Sandboxing: Conversion engines process documents within temporary Linux tmpfs RAM mounts that are isolated from other tenant worker pools.
- Automated Hard-Purge Daemon: Exactly 2 hours after completion, our background janitor daemon executes secure unlinks and memory zeroes, rendering forensic data recovery impossible.
- No Content Mining or AI Training: SwiftFileConvert explicitly guarantees that customer documents are never indexed, analyzed, or utilized to train machine learning models.
Enterprise Regulatory Compliance Matrix:
- GDPR (General Data Protection Regulation): Fully compliant with Article 32 security requirements, Data Minimization principles, and Right to Erasure mandates.
- HIPAA (Health Insurance Portability and Accountability Act): Compliant with administrative, physical, and technical safeguards for Protected Health Information (PHI).
- SOC 2 Type II: Infrastructure audited under Trust Services Criteria for Security, Confidentiality, and Availability.
Conclusion
Document security is non-negotiable. By implementing mathematically verified encryption, in-memory sandboxes, and immutable auto-purge routines, SwiftFileConvert provides enterprise security teams with unmatched peace of mind.